
You can confirm someone is over 18 without ever seeing their ID. For years, the assumption was that verification meant handing over a document, but that’s no longer true. Systems like Google’s age verification selfie analyze a face in the moment, return a result, and discard everything else. Here’s how privacy-first verification actually works, and how to bring it to your own platform.
Key Takeaways
- Verify, don’t collect. Confirming someone meets an age requirement doesn’t require knowing who they are. Skip the data and you skip the liability.
- Process it, then delete it. Real-time analysis with immediate deletion gives you a pass/fail result and nothing left to protect, leak, or subpoena.
- Say so, plainly. One sentence: “we don’t store your photo” does more for trust than an entire privacy policy page.
Why the Old Playbook Doesn’t Work Anymore
Uploading a driver’s license or passport was, for years, the default way to prove age online. It’s also become the main source of friction and risk in the process.
- ID uploads feel invasive, and for good reason; the user has to trust a stranger’s server with a scan of their government identification.
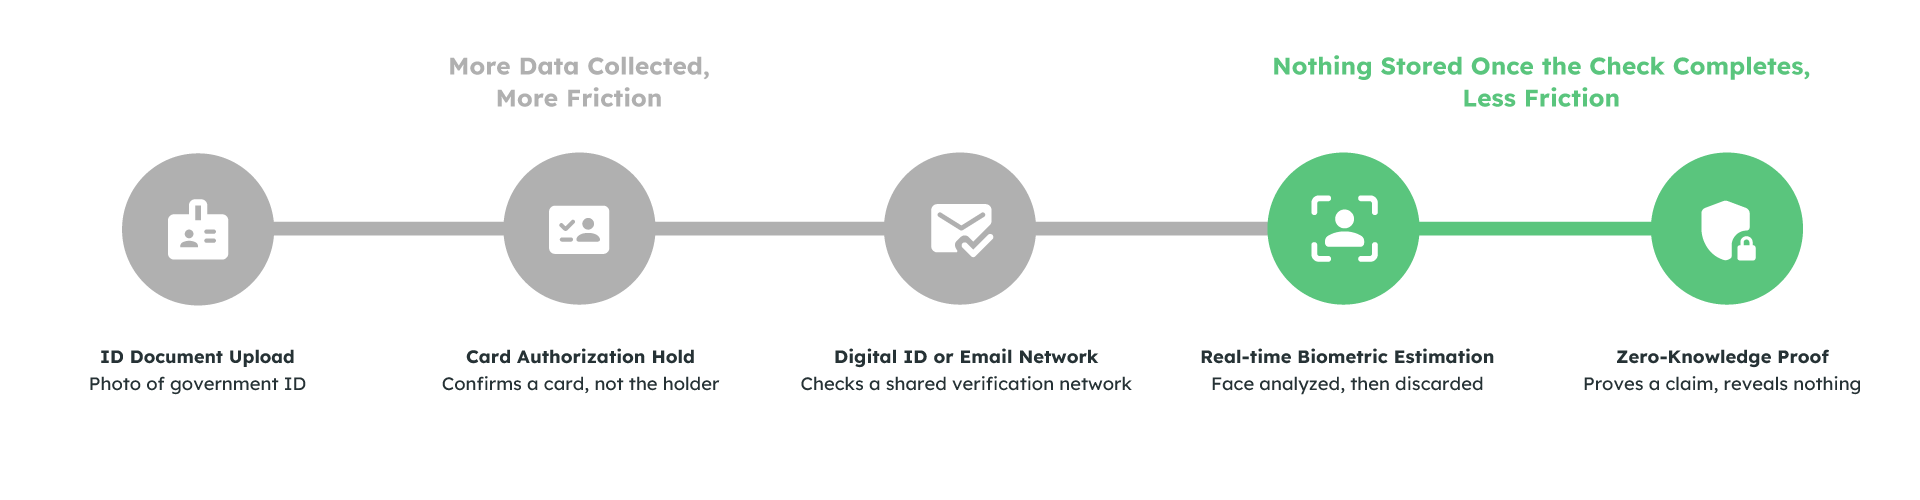
- Card checks (a small authorization hold, no charge) confirm a valid card exists, not who’s holding it; shared family cards and prepaid cards slip through.
- Digital ID and email networks check whether an email has already been age-verified elsewhere, avoiding data collection but tying accounts together across sites.
None of these were built for a world where speed, privacy, and compliance all have to hold at once.
The Real Cost of Collecting Data You Didn’t Need
Every stored ID is a future liability, not a one-time task. A breach doesn’t ask whether the data was collected for a good reason, it only needs the data to exist. Three specific risks compound this:
- Inferred age from behavior. Guessing age from browsing activity avoids an upload prompt but relies on constant tracking. A trade-off, not a fix.
- Third-party retention. Handing verification to a partner doesn’t end your exposure. If that partner keeps IDs indefinitely, their breach becomes your crisis.
- User drop-off. Friction has a cost you can measure. Every extra step to “find a wallet, pull out an ID, and take a photo of it” is a chance for someone to abandon signup entirely.
What Privacy-First Verification Actually Means
Privacy-first age verification rests on one idea: you can confirm someone is old enough without learning who they are or exactly how old they are. Three principles carry the weight:
- Minimal collection. If you don’t need the data point, don’t ask for it.
- Real-time processing. Analyze on the spot, return a result, discard the input immediately.
- Plain consent. Tell users what happens before it happens, no surprises after the fact.
This is the model VerifEye is built around: a face is analyzed for a pass/fail signal and nothing about the image is retained afterward. The platform confirms a real, unique human meets an age threshold, it doesn’t build a file on them.
“You can confirm someone is old enough without ever learning who they are.”
How Biometric Age Estimation Actually Works
Facial age estimation isn’t facial recognition. Recognition asks who someone is by matching a face against a database. Age estimation asks what; whether the face in front of the camera belongs to someone over a set threshold — and stops there.
The mechanics are simple: a user grants brief camera access, the system analyzes facial geometry against age-estimation models, returns a yes/no, and deletes the image. No upload, no storage, no facial map left behind. VerifEye runs this check in under a few seconds, with accuracy in the high 90s across age-gating use cases, reliable enough to block the overwhelming majority of underage attempts without turning signup into a chore.
Zero-Knowledge Proofs, in Plain Terms
Think of proving your age to a bouncer without showing your ID — no name, no address, no exact birthdate, just a verified “yes.” That’s a Zero-Knowledge Proof (ZKP): cryptographic math that confirms a statement is true without revealing anything beyond the statement itself.
Applied to age verification, a user holds a digital credential from a trusted issuer (a government agency, for example). Their device generates a proof that they meet the age requirement, and your platform receives a valid/invalid result — never the underlying birthdate.
“A verified yes, and nothing else — that’s the whole exchange.”
ZKPs are a strong fit where a trusted credential issuer already exists. They’re not a universal answer: without that issuer, there’s no credential to build a proof from, and the system needs a starting point before it can protect anything.
Where Each Method Sits
Zooming out, here’s how the five methods this piece has covered compare on the two things that matter most: how much data they collect, and how much friction they add.
Weighing Accuracy Against Fairness
Accuracy numbers only tell half the story. The Electronic Frontier Foundation has flagged that age-estimation systems can perform less reliably for people of color, transgender and nonbinary individuals, and people with disabilities — which means an “accurate” system can still lock out legitimate users unevenly. That’s not a rounding error; it’s a fairness problem that shows up as a support ticket, a lost signup, or a headline.
“A system that’s accurate for most people is still failing the rest.”
Closing that gap takes deliberate work; testing across demographics and training on datasets built for balance, not convenience. VerifEye’s models are trained specifically for fairness across skin tones and demographics, not just overall accuracy, because a check that works for 95% of people isn’t done until it works for the other 5% too.
Choosing the Right Method for Your Platform
There’s no universal answer, the right method depends on your industry, your legal exposure, and how much friction your users will tolerate before they leave.
- Accuracy vs. privacy: tighter certainty usually asks for more information; a lighter touch trades some precision for speed.
- Implementation lift: a simple API integrates faster than a full SDK build — know which one your team can realistically ship.
- Total cost: per-verification fees and subscriptions both carry a cost, but a clunky process costs you in lost signups regardless of price.
Rolling it out: what actually builds trust
Introducing verification is a conversation with your users as much as a technical change. Three things matter most:
- Explain before you ask. State plainly why verification exists and what happens to the data. Vague explanations create the drop-off you’re trying to avoid.
- Show the deletion, don’t just claim it. Say explicitly that the photo is analyzed and discarded — not “processed,” not “reviewed.”
- Warn users about phishing. Make clear you’ll never request an ID photo by email. Legitimate checks happen inside a signed-in session.
FAQ
- How can age be verified without storing my photo? The camera captures a live image, an algorithm estimates age from facial characteristics, and the image is deleted the moment a pass/fail result is produced. Nothing is retained.
- Is this compliant with laws like the UK’s Online Safety Act? Most regulations set a verification standard to meet without mandating a specific technology, which gives platforms room to choose privacy-preserving methods that also satisfy the legal requirement.
- Is facial age estimation the same as facial recognition? Recognition identifies who you are; age estimation confirms what age bracket you’re in, without ever trying to determine identity.
- How accurate is it? High-quality systems land in the 95–99% range for determining whether someone is over 18, enough to block the large majority of underage attempts while keeping the process quick.