
Fraud teams rarely lack signals. They lack the right signal at the right decision point, especially when automated activity looks convincingly human. A fraud detection API can add human-presence and uniqueness signals to an existing risk decision, helping separate a genuine person from spoofing attempts or duplicate-account activity. The result is one more input for the risk engine, not a verdict about identity or intent.
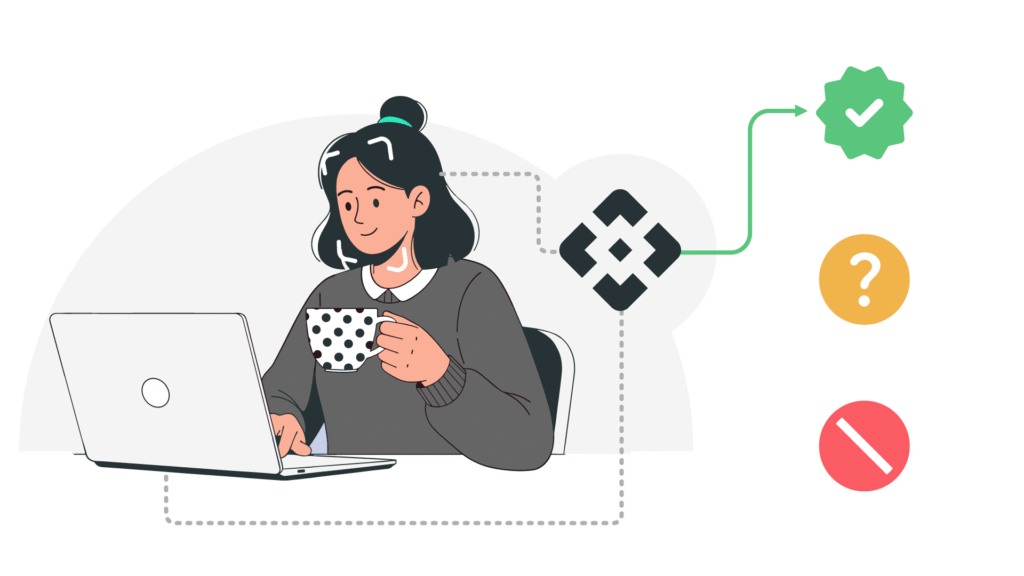
The practical work is architectural: a user gives consent, verification runs, and the application receives a status plus permitted metadata that informs an allow, block or review outcome. The quality of that integration depends on understanding what each signal means and where it belongs in the flow.

Why Add a Human-Presence Signal to Fraud Decisions?
Most fraud systems already examine useful evidence: device intelligence, behavioral analytics, account history, transaction context and rules built around known abuse patterns. The remaining question is simpler: is there a real person present at the point where the signal matters, or is the system interacting with automation, a replay or a synthetic workflow?
That question doesn’t replace risk scoring, it adds another layer of evidence. VerifEye positions human-presence and uniqueness signals as enrichment for existing rules engines, device intelligence, behavioral analytics and human review. The risk engine still decides whether to allow, block or review an event — the fraud detection API signal only informs that decision.
What liveness, uniqueness and identity verification each answer
These capabilities answer different questions, and keeping them separate makes downstream rules easier to explain, test and govern:
- Liveness: is the interaction coming from a live person rather than a photo, replayed video or deepfake? VerifEye Onboard confirms real human presence and flags spoofing attempts.
- Uniqueness: is this person creating another account within the same user base? Uniqueness validation compares privacy-preserving facial signatures to help prevent duplicate account creation.
- Identity verification: can the person be linked to a claimed identity? That’s a separate task from establishing human presence, and a liveness result alone shouldn’t be presented as legal identity proof.
Age estimation, where used, is a further distinct signal that can support an eligibility decision. It isn’t a substitute for identity verification, or a full description of the person behind an account.
Where this matters most: synthetic identity fraud
A fabricated profile can pass checks based on plausible attributes while still creating problems through automation, repeated account creation or coordinated abuse. Human presence and uniqueness expose parts of that pattern a single attribute or device signal can’t catch alone — see our related post on synthetic identity fraud detection for a closer look.
NIST notes that attribute validation services can support secure identity proofing, access control and fraud prevention, provided they’re validated against reliable data sources. The lesson for any production risk system is the same: evidence has a role and a confidence boundary. Liveness detection signals give a fraud detection API a more relevant view of the interaction, but the final decision should still combine that signal with account, device, behavioral and human-review context.
Where Does the Fraud Detection API Signal Belong in a Risk Architecture?
A human-presence signal is most useful when it arrives at the point where a risk decision needs more context, and least useful when bolted onto every interaction by default. Map the customer journey first, and identify events where automated activity, account duplication or spoofing would materially change the risk profile.
Mapping the Fraud Detection API Signal to Key Journey Events
Signup is often the clearest starting point, and maps directly to VerifEye Onboard: a liveness result helps distinguish a real person from a photo, replayed video or deepfake, while a uniqueness result adds context when the same person appears to be creating multiple accounts. Neither result alone proves legal identity or malicious intent.
The same signal is useful later in the journey too. At login, it can support a step-up decision when device or behavioral signals change — this is where VerifEye Reverify fits. Before a payment or other high-risk action, VerifEye Protect adds human-presence context to transaction, account and session signals. During account recovery, VerifEye Recover helps determine whether a request merits additional verification. Placement depends on the threat model, the friction budget and the cost of a false positive.
| Signal role | Useful event | Decision contribution |
|---|---|---|
| Liveness | Signup, login step-up, recovery or a high-risk action | Raises or lowers confidence that a real person is present, alongside device and behavioral evidence |
| Uniqueness | Signup or account reactivation | Adds context for possible duplicate-account creation without treating duplication as proof of fraud |
| Permitted metadata | Any event where the risk engine needs correlated verification context | Supports consistent scoring, policy evaluation, audit trails and targeted step-up or review |
Keep the decision layer simple
The workflow stays simple at the decision layer: collect consent, run the verification step, receive a status and permitted metadata, then combine those outputs with the signals already in the risk engine. A result consistent with a new, verified account can support an allow decision. A duplicate result can raise risk or trigger a policy-specific step-up. An ineligible or terminated session can route to review, retry or block, depending on the surrounding evidence.
Treating one signal as an automatic verdict creates brittle policies and turns uncertainty into unnecessary customer friction. NIST recommends an incremental, risk-based approach to API protection across development and runtime, and the same discipline applies here: define the event, document what the signal means, set an appropriate response and keep a human review path for ambiguous cases. See our guide on bot detection versus liveness for account fraud for the distinction between automated bot detection and human-presence verification.
In practice, the best architecture is layered: does the activity look automated, is a real person present, does the account or identity appear unique, and does the overall behavior fit the business context? NIST’s API security guidance supports this incremental, risk-based view of controls.
What Should a Fraud Detection API Return to the Risk Engine?
A useful response doesn’t pretend to be a final fraud verdict, it gives the risk engine a small, well-defined set of signals to evaluate alongside device intelligence, behavioral analytics, account history and human review.
The status vocabulary should be explicit enough that downstream teams can act consistently. In VerifEye’s documented examples, OK represents a newly verified account, Duplicate indicates a duplicate account, NotEligible covers cases such as invalid imagery or automation behavior, and Null can indicate a terminated session. Confirm the current API contract before hard-coding status handling — these are illustrative outcomes, not a guaranteed endpoint contract.
Return signal meaning, not unnecessary identity data
Permitted metadata should be limited to what the risk decision needs: the verification status, an event or session reference and a result relevant to uniqueness or human presence. VerifEye’s architecture uses on-device or in-memory processing without persistent image storage, and transmission limited to metadata or numeric feature vectors, supporting a data-minimization approach. Confirm the exact fields, retention rules and permissions for your implementation with engineering and compliance.
That same opt-in principle now runs through VerifEye’s unified Face API: a single endpoint returns only the attributes a call requests, so a fraud detection API integration stays as lean as the risk decision actually needs.
Liveness, uniqueness, age estimation and identity verification are different signals. A response that indicates human presence doesn’t establish legal identity, and a uniqueness result doesn’t by itself prove an account is trustworthy. See how to prove a user is human without turning a fraud check into an identity dossier.
Make responses safe to retry and easy to trace
Every verification result should correlate to the original business event through a stable request or session identifier, so investigators can connect the signal to signup, login, payment, recovery or another high-risk action without relying on timestamps alone.
Idempotency matters when clients retry after a timeout or a queue delivers the same event twice: define whether a repeated request reuses the prior result, creates a new session or returns a controlled duplicate response. Error handling needs the same discipline — validate authentication and signature controls, and distinguish invalid input, expired sessions, authorization failures, unavailable dependencies and terminated flows. VerifEye documents JWT authentication for verify-duplicate operations, API key management and signature validation for redirect flows.
Finally, define a fallback before production traffic arrives. An unavailable human-presence signal should route to an existing risk policy, step-up check or review queue according to transaction risk — it shouldn’t silently become an allow decision, and it shouldn’t automatically become a block just because the signal is unavailable.
How Do You Manage Fraud Detection API Latency, Privacy and False Positives?
A useful fraud detection API depends on where verification runs, what the risk engine receives, and what happens when the signal is uncertain. Set a latency budget for each user journey before implementation: a signup flow may tolerate a different interaction cost than a payment authorization or account recovery. Measure the complete path, including client collection, network time, service processing, risk evaluation and any human-review queue.
Choose synchronous and asynchronous moments deliberately
Use a synchronous check when the decision must gate a high-risk action, such as creating an account, recovering access or completing a sensitive transaction. Keep the response narrow and define timeout behavior before launch — a timeout shouldn’t quietly become an inconsistent allow decision, it should route through the same policy used for other missing or inconclusive signals.
Asynchronous verification can reduce friction when the signal is useful for enrichment rather than immediate enforcement. A platform can collect an approved signal during an earlier step, attach a correlation identifier and apply the result when a later event reaches the risk engine, provided retention, replay and expiry rules are clear. See NIST’s API protection guidance when defining those controls.
Minimize data before it reaches the risk engine
Start privacy review with the decision that must be made, not with every field a provider could expose. VerifEye’s architecture uses on-device or in-memory processing, without persistent image storage, with transmission limited to metadata or numeric feature vectors — confirm the actual data flow, retention period, access controls, deletion behavior and processor responsibilities with engineering and compliance.
Keep human presence distinct from identity proofing. Liveness helps detect attempts involving photos, replayed video or deepfakes, while uniqueness helps identify duplicate account creation — neither should silently become a claim about legal identity. Privacy review should also cover consent withdrawal, regional requirements, accessibility and what happens when a user can’t complete the verification step.
Calibrate uncertainty instead of turning it into a block
False positives are a policy problem as much as a model problem. Start with a step-up path for ambiguous outcomes: request another signal, delay the action for review or ask a trained analyst to inspect the case. Compare outcomes by cohort, device context, geography and journey, and track approval rate, abandonment, confirmed fraud, review volume and reversals together. A threshold that reduces fraud while creating an unacceptable support burden isn’t an operational win.
Human-presence verification should strengthen rules, device intelligence, behavioral analytics and human review, not replace them. Test the signal in shadow mode first with VerifEye Protect, then introduce enforcement only where the evidence supports it.
How Should Teams Measure a Safe Fraud Detection API Rollout?
A human-presence signal should earn its place through measured improvement, not a dramatic launch-day switch. Treat the rollout as an experiment layered onto the existing risk engine — VerifEye is positioned as enrichment for rules, device intelligence, behavioral analytics and human review, not a replacement for them. That distinction keeps the measurement honest: does the combined system make better decisions for the business and for legitimate users?
Establish the baseline, then run in shadow mode
Record current rates and business impact for the journey under review: fraud loss, legitimate approvals, abandonment, manual-review volume and time to resolve reviewed cases, segmented by journey, geography, device context and customer tenure. Establish the observation window and decision owner before adding the new signal.
Then collect consent and run verification without letting its output change the customer-facing decision yet. Compare the signal with confirmed fraud outcomes, chargebacks, account investigations and review findings. This shows where human presence adds useful information and where it overlaps with existing controls. Keep liveness, uniqueness, age estimation and identity verification separate in the analysis, since none should become the sole risk criterion.
Expand through controlled cohorts and calibrated thresholds
Start with a clearly bounded cohort, such as a selected traffic source, transaction band or new-account flow, and preserve a comparable holdout where practical. Expand only when the first cohort shows stable results across approval, abandonment, fraud loss and review load.
Begin with conservative uses of the output: a high-confidence combination of signals may support an allow or block path, while ambiguous cases go to step-up or human review. Reassess thresholds against observed outcomes rather than optimizing one metric in isolation — the best threshold isn’t the one that blocks the most activity, it’s the one that reduces meaningful fraud without an unacceptable burden for legitimate users or reviewers.
Set rollback criteria and keep a record
Define the thresholds that pause or reverse the rollout, including a material increase in abandonment, false blocks, fraud loss or review backlog, and specify who can trigger a rollback and how the prior decision path is restored. A Kantar deployment cited by Realeyes reports 96% fraud detection and 0.67% false positives — useful context, not a universal benchmark for a new deployment. Teams looking beyond automated abuse should also read how to stop human fraudsters, since a human-presence signal is one layer in a broader defense.
Review results at a fixed cadence, retain the cohort definitions and threshold changes, and document the evidence behind each expansion. That record turns a fraud detection API integration from an opaque control into an accountable risk decision.
Frequently Asked Questions
Is a fraud detection API a replacement for existing risk controls?
No. Human-presence and uniqueness results work best as additional signals alongside rules, device intelligence, behavioral analytics and human review. The risk engine combines those inputs to support an allow, block or review decision rather than treating one verification result as a final verdict. See how VerifEye fits into a risk stack.
What is the difference between liveness and uniqueness?
Liveness confirms that a real person is present and helps identify spoofing attempts involving photos, replayed video or deepfakes. Uniqueness addresses whether the same person is creating multiple accounts, using privacy-preserving facial signatures across a defined user base. Neither capability alone proves legal identity.
What should an engineering team do with a verification result?
Map the result to an existing risk policy. A positive human-presence result may lower risk, while a duplicate or ineligible result may trigger a step-up check, manual review or a block. VerifEye documents outcomes that map naturally to workflows, including OK, Duplicate, NotEligible and Null, but confirm the current API contract before hard-coding status handling.
Can verification be implemented without retaining face images?
Yes, in VerifEye’s architecture: on-device or in-memory processing, no persistent image storage, and transmission limited to metadata or numeric feature vectors. Engineering and privacy teams should still define consent, retention, access and fallback rules for the complete implementation, not just the verification call.